46 Accounts, No Alerts: KYC's $40B Deepfake Gap
A new report puts deepfake fraud at $40B. The ABN AMRO breach — 46 fake accounts before any alert — is the clearest sign that static KYC is losing.

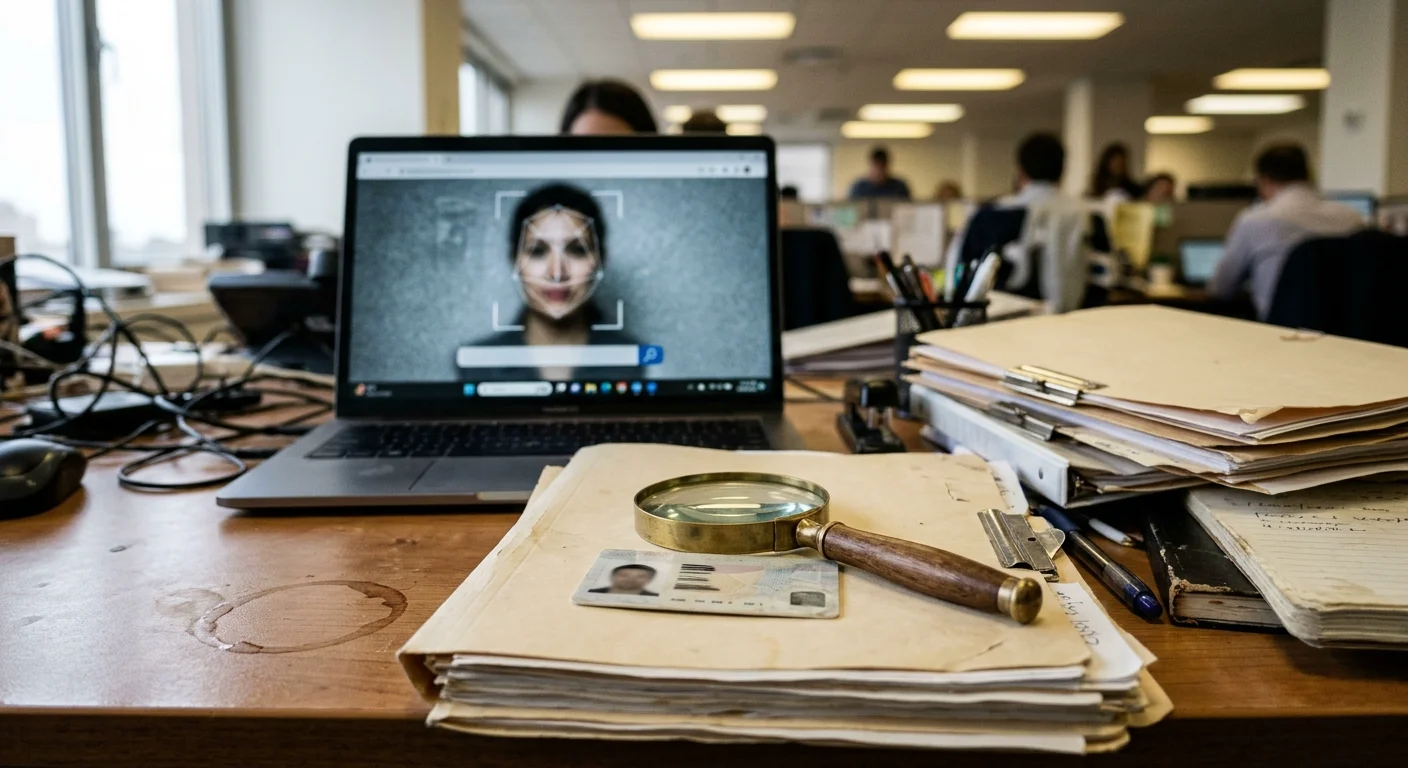
On March 23, 2026, Dutch prosecutors charged a 34-year-old Amsterdam man with opening 46 bank accounts at ABN AMRO using a technique that bypassed the bank's automated identity checks every single time: a deepfake selfie morphed to match a stolen ID document.
The forty-sixth account was caught not because the system flagged a suspicious pattern, but because one application paired a female passport photo with a male selfie — a cosmetic mismatch, not a synthetic fraud detection. Remove that coincidence and the count could have been 50, or 60, or more.
This case is not a curiosity. It is a controlled experiment in KYC failure. And it arrived in the same year as a report that frames it as part of a $40 billion industry-wide crisis.
The $40 Billion Wake-Up Call
On October 13, 2026, deepfake detection company identifAI published what it describes as the first comprehensive measurement of deepfake-enabled financial fraud. The headline figure — $40 billion per year — is a vendor estimate and should be treated with appropriate skepticism. The specific data points inside the report are harder to dismiss.
Identity fraud now accounts for 17.6% of all deepfake fraud incidents globally. Synthetic media causes 1 in every 100 identity verification check failures — a figure independently corroborated by LexisNexis Risk Solutions in July 2026, as we examined in how deepfakes are breaking ID checks at scale.
Video and voice cloning account for nearly two-thirds of observed synthetic fraud cases. The United States is the largest target at 34.1% of incidents, followed by India at 7.7% and the UK at 6.6%.
The ABN AMRO breach sits squarely inside this data. It is the case that turns the statistics into something concrete.
How the Attack Worked
ABN AMRO's mobile onboarding flow — like most retail bank onboarding flows as of early 2026 — required two inputs: a photo of a government-issued ID, and a selfie to verify the applicant's face matched the document.
According to court records and analysis published by iProov, the attacker obtained stolen identity documents from multiple sources, with some reportedly harvested via a TikTok campaign that offered cryptocurrency payments in exchange for selfie videos. For each account application, he submitted the stolen ID alongside a deepfake selfie — his own face digitally morphed to resemble the photo on the document.
The bank's automated face-matching system accepted each match. It was not designed to detect morphing signatures or injection artifacts. It was designed to answer one question: does face A match face B? The attacker simply made the two faces look similar enough.
The system worked exactly as specified. The specification was wrong.
This flaw is not unique to ABN AMRO. Any KYC workflow that treats selfie-to-document matching as its terminal check is architecturally exposed to this class of attack. The attacker does not need to defeat a particularly sophisticated detector — only to satisfy its narrow success criterion.
Why Static KYC Cannot Catch This
Traditional identity verification operates at a single moment in time. A customer submits documents and a selfie during onboarding. The system compares face to photo, reads the document fields, runs a liveness check, and either approves or rejects.
Every step in that flow targets artifacts: the document image, the selfie, the liveness signal. Modern deepfake tools are specifically designed to produce plausible artifacts for each check. Commercial KYC bypass toolkits are sold on darknet markets for as little as $15, complete with tutorials for defeating the liveness detection used by the major verification platforms.
The deeper architectural problem is that static verification has no behavioral baseline. It cannot ask: does this applicant behave like someone who has legitimately operated a bank account before? Is the device fingerprint consistent with similar customers? Does the velocity of account openings across the institution suggest a coordinated pattern?
In the ABN AMRO case, a behavioral and cross-account analysis would have surfaced the coordinated pattern well before account 46. The attacker was operating at scale by definition — which generates cross-application signals that point-in-time verification is structurally unable to see.
| Verification approach | What it checks | What it misses |
|---|---|---|
| Document scan | Forgery artifacts, data fields | Morphed selfie matched to stolen ID |
| Liveness detection | Real-time presence | Identity of the live person |
| Face matching | Selfie-to-ID similarity | Similarity manufactured through morphing |
| Static onboarding | Single-moment snapshot | Cross-account coordination patterns |
What the identifAI Report Recommends
The report makes four recommendations relevant to identity verification teams.
Use separate verification channels for high-value transactions. A deepfake may bypass onboarding, but a second verification step using a different signal — device history, behavioral baseline, a distinct biometric modality — raises the attack cost significantly.
Move from document verification to credential verification. Document images are synthesizable. EU-recognized electronic identification schemes, including the EUDI Wallet, are cryptographically bound to the issuing authority and cannot be morphed or injected.
Add behavioral context. Account velocity, device-sharing patterns, and session behavior are signals that deepfake tools cannot currently replicate convincingly at the scale required for coordinated fraud.
Automate the correlation layer. A human analyst reviewing 50 individual account applications will not see the cross-application pattern. An automated system ingesting all 50 simultaneously will.
This last point is where multimodal liveness detection alone proves insufficient. Liveness answers one narrow question — is this image live and present? — but not the more important one: is this applicant who they claim to be, in context, across applications?
The Regulatory Response
ETSI released TS 104 275 in September 2026, a technical specification that for the first time places affirmative obligations on developers of generative AI systems to prevent those systems from producing harmful deepfakes. Requirements include pre-release risk assessment, output content filtering, AI-generated content labelling, and incident documentation across five phases of the AI lifecycle.
The standard does not directly govern KYC providers, but it shifts liability upstream: AI vendors supplying synthetic media generation tooling will now face compliance obligations that did not previously exist. This raises the cost of developing deepfake-for-fraud toolkits and creates an audit trail for enforcement agencies to follow.
The EU's AMLR, taking effect July 2027, treats identity verification as a core due-diligence obligation for all financial institutions and crypto-asset service providers. Under draft AMLA technical standards published in late September 2026, electronic identification — eID schemes and the EUDI Wallet — becomes the preferred route for remote customer onboarding, with document-based checks requiring explicit justification when used as a fallback.
Had the ABN AMRO breach occurred under AMLR rules, regulators would have clear grounds to question whether a document-plus-selfie workflow was adequate given the known vulnerability class.
Closing the Gap With Autonomous Agents
The ABN AMRO case illustrates the structural limit of rule-based, point-in-time verification. Closing that limit requires a system that operates continuously, across applications, correlating signals that no individual check can access.
Agentic KYC — the model that replaces static verification queues with autonomous AI agents — is built for this architecture. Joinble's AI agents ingest behavioral signals, device data, cross-customer correlation, and continuous monitoring events in parallel, surfacing coordinated fraud patterns before they accumulate into 46 accounts.
The objective is not a better liveness check. It is a system that asks fundamentally different questions — questions that synthetic media, however sophisticated, cannot currently answer convincingly at the account-opening scale this kind of fraud requires.
The attacker who opened 46 ABN AMRO accounts relied on a system that asked exactly one question, 46 times in isolation. The answer to that case is not a better question. It is a better system.
Frequently Asked Questions
What was the ABN AMRO deepfake fraud case?
A 34-year-old Amsterdam man was charged in March 2026 with opening 46 ABN AMRO bank accounts using deepfake selfies matched to stolen ID documents. The bank's automated face-matching system accepted all 46 applications because it detected no morphing or injection artifacts — it only checked whether the selfie matched the ID photo.
How large is the deepfake fraud problem globally?
identifAI's October 2026 report estimates deepfake-enabled financial fraud at $40 billion per year globally. Identity fraud specifically accounts for 17.6% of incidents. The US is the largest target at 34.1% of cases, followed by India and the UK.
Why did liveness checks not catch the ABN AMRO fraud?
Standard liveness checks test whether an image is live — presented in real time, not replayed from a recording. They do not test whether a face has been morphed to match a specific ID document. The attacker exploited this gap: a live, morphed face satisfies a liveness check while bypassing identity matching.
What is ETSI TS 104 275?
ETSI TS 104 275, published in September 2026, places obligations on developers and operators of generative AI systems to prevent their tools from producing harmful deepfakes. Requirements include pre-release risk assessment, output filtering, content labelling, and incident documentation across the full AI lifecycle.
What does the EU AMLR change for identity verification?
AMLR, effective July 2027, mandates identity verification as a core due-diligence obligation for financial institutions and crypto-asset service providers. Draft AMLA technical standards make eID-based onboarding the default remote route, reducing reliance on document-plus-selfie workflows that are vulnerable to morphing attacks.
How do autonomous AI agents improve deepfake fraud detection?
Autonomous AI agents ingest cross-application behavioral signals, device fingerprints, and network-level patterns simultaneously — signals that static, point-in-time verification cannot access. This cross-account correlation layer catches coordinated fraud far earlier and at lower per-check cost than human review, closing the gap the ABN AMRO case exposed.
Related Articles
The 45-Day Mule Account Gap: Why FRAML Needs Agentic AI
Money mule accounts stay active 45 days before detection. Here is how FRAML convergence and agentic AI are closing the gap for banks in 2026.
IDScan.net Breach: 153M IDs and the KYC Vendor Gap
The IDScan.net breach exposed 153 million driver's licenses in September 2026 — a case study in why outsourced KYC creates third-party identity risk.
The $40B AI Fraud Crisis: The Industry Fights Back
Deloitte projects AI-enabled fraud will reach $40 billion by 2027. Here is how the financial industry's landmark 20-point plan reshapes KYC compliance.