Why Liveness Detection Fails Against Injection Attacks
Injection attacks feed deepfakes into KYC APIs, bypassing liveness checks at the software layer. The WEF 2026 Atlas tested 17 tools that defeat standard biometric verification.
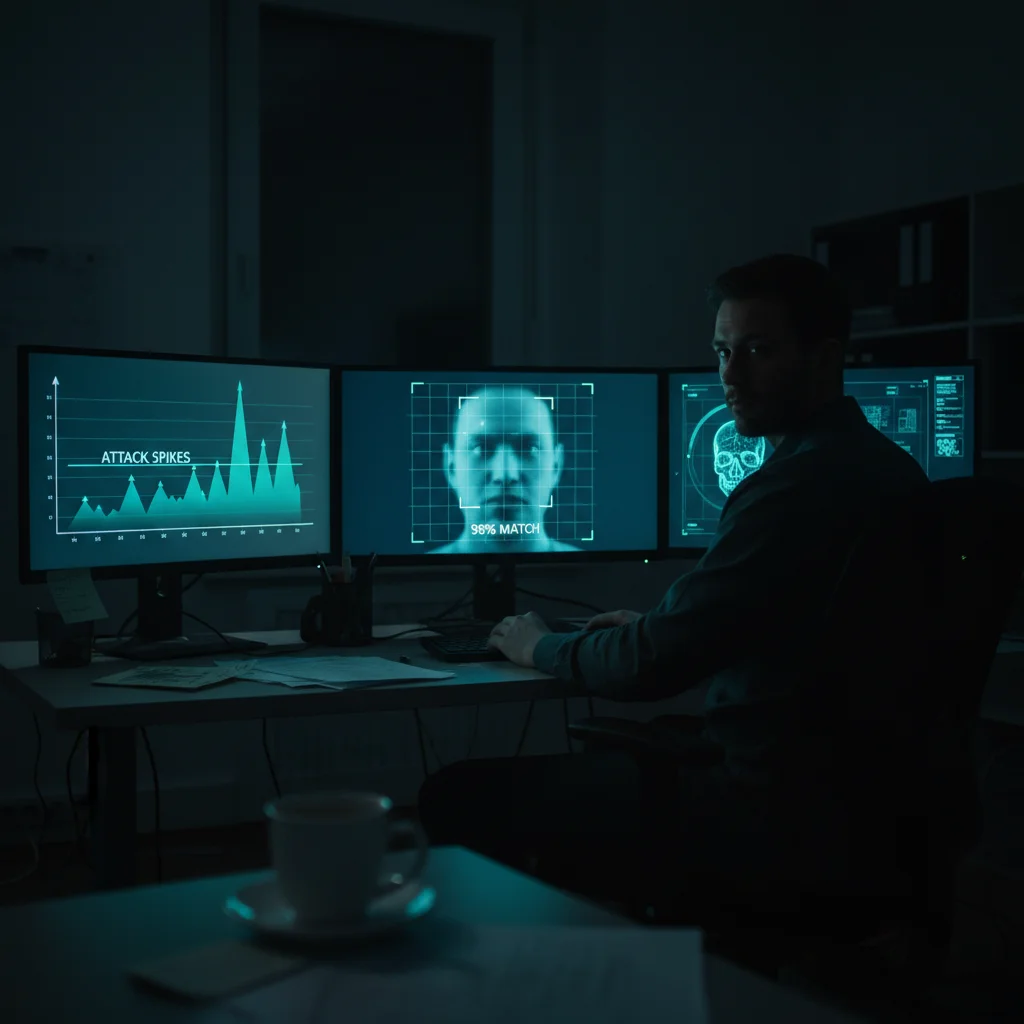
Liveness checks added to onboarding flows once looked like a definitive answer to deepfake fraud for identity verification platforms. A smile, a head turn, a selfie video — evidence that a real human sat behind the camera. That assumption now fails in a systematic way.
The threat landscape has been rewritten by camera injection attacks. Attackers no longer hold a deepfake video in front of a physical camera; they skip the camera altogether and feed synthetic faces straight into the application's biometric API. The liveness check still executes. The synthetic face still clears it. Nobody is watching.
Seventeen face-swapping tools and 8 camera injection tools were tested against commercial biometric onboarding systems in the World Economic Forum's Cybercrime Atlas report, published in January 2026. The finding was blunt: standard liveness checks were successfully bypassed by most tools.
How injection attacks work, why conventional liveness detection cannot stop them, and what a genuinely resilient verification architecture requires in 2026 are what this article explains.
The Technical Split That Undoes Liveness
What liveness detection was built to stop is the starting point for why it fails.
Presentation attacks are physical. In front of the camera, a fraudster holds a printed photo, plays a pre-recorded video on a screen, or wears a silicone mask. Depth anomalies, texture inconsistencies, and lighting artifacts that indicate something artificial is in frame are what Presentation Attack Detection (PAD) algorithms look for as they analyze biometric data from the physical sensor.
Against presentation attacks, PAD works. Against injection attacks, it fails entirely.
The camera is never touched by an injection attack. Instead:
- Commercially available AI face-swapping tools are used by the attacker to generate a deepfake video.
- Virtual camera software — OBS, ManyCam, or specialized injection toolkits — presents that synthetic video stream to the operating system as a legitimate camera input.
- Directly into the application's API pipeline, the synthetic biometric data is injected, bypassing the physical sensor.
Perfectly structured biometric data reaches the PAD algorithm, because it arrives through the same data pathway as genuine camera input. Real sensor data and injected synthetic data cannot be distinguished by the algorithm at the software layer. Detecting physical fraud is what it was designed to do — not this.
That architectural blind spot is what injection attacks exploit, and making liveness detection more sophisticated cannot close it. PAD algorithm quality is not the problem. The PAD algorithm is inspecting the wrong layer of the stack.
How Large the 2026 Threat Has Become
Threat severity is no longer ambiguous once the numbers are on the table.
8,065 biometric injection attacks were documented by threat-intelligence firm Group-IB against the KYC onboarding flow of a single financial institution between January and August 2025 — more than 38 attacks per day against one organization.
Tooling that enables this industrial-scale fraud was mapped by the WEF Cybercrime Atlas, published in January 2026. Researchers examined 17 face-swapping tools and 8 camera injection utilities — commercially available products, requiring no advanced technical expertise. Most tools successfully bypassed standard biometric onboarding systems that relied on liveness detection alone: that was the conclusion.
Economics make the problem worse. Injection attacks, unlike sophisticated cyberattacks that require rare skills, are cheap and scalable:
| Attack Component | Cost |
|---|---|
| AI face-swapping tool (per session) | $10–$50 |
| Assembled synthetic identity | ~$15 |
| Virtual camera software | Free–$30 |
| Technical skill required | Low |
"Face alone is no longer proof of identity." That is how a Biometric Update report from April 2026 put it, directly.
A marginal threat this is not. Remote identity verification's primary attack vector in 2026 is this one, and liveness detection — the industry's primary defense — does not address it.
Where the Industry Misallocated Effort
Heavy investment in PAD has been the KYC industry's response to deepfakes, and that investment has been largely misdirected against the actual threat.
The presentation attack problem that dominated 2019–2021, when most deepfake fraud involved physical displays of generated content, is what PAD was built for. Certified solutions proliferated as the ecosystem matured, and liveness checks became a standard component of remote identity verification inside compliance frameworks.
Attackers, meanwhile, shifted to injection attacks, which render the liveness layer irrelevant.
Compliance frameworks move slowly, and that is the structural reason for this lag. Most regulatory guidance on remote biometric verification was written before injection attacks became a practical threat. "Reliable" identity verification is what the AMLR requires — but the technical architecture that counters injection attacks at scale is not yet specified in the Regulatory Technical Standards (RTS) being finalized now.
Many compliance teams have therefore checked the "liveness detection" box without grasping that they have checked the wrong box for the threat that currently exists. Protection against presentation attacks is what the ISO standard for biometric presentation attack detection — ISO 30107-3 — certifies. Injection attack resistance is not mentioned. Certification does not equal protection until ISO/IEC AWI 30107-4 (which addresses injection vulnerabilities) is finalized and adopted.
Architecture That Actually Resists Injection
Moving from single-signal biometric verification to a multi-layer architecture that does not trust any single data source is what countering injection attacks requires.
Layer 1: Device Attestation
The injection vector is addressed directly by the first layer. Cryptographic verification that biometric data originates from a real hardware sensor on a real device — not from virtual camera software or an API injection — is what device attestation provides. Modern mobile operating systems supply the infrastructure for this:
- iOS: Server-side verification that biometric data is captured on a genuine Apple device running unmodified software is available through DeviceCheck and AppAttest APIs.
- Android: Equivalent hardware-bound attestation is provided by Play Integrity API.
- Web-based flows: Partial coverage comes from hardware security modules and browser attestation APIs (WebAuthn), though the attack surface is wider.
Any system that trusts biometric data at the software layer can be defeated by injection without device attestation. With it, hardware-level security must be compromised by an attacker — a materially higher threshold.
Layer 2: Behavioral and Environmental Signal Analysis
A biometric match is not the whole of genuine identity verification. Characteristic behavioral patterns show up in legitimate users: natural interaction timing, realistic form navigation, device orientation changes consistent with a person holding a phone. Session-level anomalies typically appear when fraudsters use automated injection tooling — anomalies invisible to biometric analysis but detectable through behavioral signal analysis.
Sessions that pass biometric checks yet show environmental inconsistencies can be flagged by AI systems analyzing these signals in real time — unusual metadata, mismatched device clocks, network fingerprints associated with known fraud infrastructure, or interaction patterns that match automated tooling rather than human behavior.
Layer 3: Cryptographic Document Binding
Document verification combined with biometric verification has been standard practice for years. Cryptographic verification of the document itself is what changes the equation — reading the NFC chip embedded in most modern passports and national ID cards to verify that:
- Tampering with the chip has not occurred (verified against the issuing government's certificate authority).
- The live biometric capture matches the face stored on the chip.
The attack bar rises dramatically. A genuine NFC-chipped document containing that face, not merely a convincing synthetic face, is what an attacker must produce to defeat a cryptographically bound document-biometric check. Physical document forgery is required, which is a different order of complexity and cost.
Layer 4: Continuous Post-Onboarding Monitoring
Accounts, not a one-time identity check, are what injection attacks are designed to create. Institutions that verify at onboarding and then trust the resulting account implicitly face a risk that compounds over time: synthetic identities that pass onboarding, establish behavioral history, and execute fraudulent transactions months later — after risk scoring has normalized.
This model is changed fundamentally by autonomous AI agents. Identity verification is no longer treated as a point-in-time checkpoint; Joinble's AI agents continuously monitor account behavior against the identity baseline established at onboarding — detecting behavioral drift, re-triggering identity verification when risk signals escalate, and escalating to human review only for genuinely ambiguous cases.
A verification gate becomes an identity management system under this shift. Our analysis of how autonomous AI agents are replacing manual compliance reviews looks in detail at how agentic KYC differs from traditional AI-assisted verification.
Regulation Still Catching Up
July 2027 is when the AMLR's requirements for reliable identity verification apply, but "reliable" will be defined in technical terms by the RTS being finalized now. Existing eIDAS framework standards — written before injection attacks became a primary threat vector — are largely what current AMLA draft standards follow.
A compliance blind spot follows: KYC infrastructure built to current regulatory requirements may leave organizations technically compliant but operationally vulnerable to the actual threat landscape.
Enhanced identity verification is required by MiCA's KYC requirements — applying to all CASPs in the EU from December 2024, with the transitional window closing July 1, 2026 — yet those rules similarly predate the injection attack era. Delivering both regulatory compliance and genuine security at once is the challenge for crypto firms navigating MiCA compliance while building fraud-resistant onboarding. What the forthcoming technical standards will require of identity systems is covered in our analysis of AMLA's CDD RTS.
PAD Certification as False Comfort
ISO 30107-3 certification is displayed prominently by many identity verification vendors. For presentation attacks, that certification matters. Against injection attacks it provides no assurance, and vendors who present it as comprehensive protection are either unaware of the distinction or are not being transparent about it.
Direct questions should come from procurement teams evaluating KYC technology in 2026:
- What device attestation methods does your system use?
- How does your system detect virtual camera injection at the session level?
- What behavioral signal analysis runs alongside biometric verification?
- Has the system been tested against injection attack toolkits, and what are the results?
- Does the system support NFC-based cryptographic document verification?
A starting point, not an answer, is what PAD certification is. The threat has moved on.
Building Around the Threat That Is Here
Solving the last problem while the next one scales is a recurring pattern in the identity verification industry. 2020's threat met the right answer in presentation attack detection. 2026's threat does not.
Those that treat identity verification as a continuous system will be the organizations that navigate this landscape successfully — combining device attestation, behavioral analysis, cryptographic document binding, and ongoing monitoring into a layered architecture that does not assume any single signal is reliable in isolation.
Our earlier piece on deepfakes in banking onboarding gives context on how the deepfake tooling ecosystem has developed from the fraud industry's side. Darknet economics of identity fraud as a service are covered in our analysis of KYC bypass-as-a-service. A further evolution of this threat emerged in April 2026: the Mercor breach showed how attackers are now targeting raw biometric training data at scale — creating pre-assembled impersonation kits that bypass the document and voice layers simultaneously. How the industry responded in July 2026 — with multimodal architectures from Regula and physio-behavioral AI from AU10TIX — is covered in our analysis of why no single biometric signal wins in 2026. Systemic scale implications — LexisNexis data showing 1 in 100 failed identity checks now involves a deepfake at 100 billion annual checks globally — appear in our August 2026 analysis of how deepfakes are breaking identity verification at infrastructure scale.
How the industry's detection standards are evolving in response — from single-signal face verification to cross-modal multimodal liveness architectures — is covered in our analysis of why face alone is no longer proof and what multimodal liveness verification requires.
A face on its own no longer suffices. Whether your verification stack is built around that reality remains the question.
Frequently Asked Questions
What is a KYC injection attack?
Synthetic biometric data — typically a deepfake face or video — is inserted by an injection attack directly into an application's biometric API pipeline, bypassing the physical camera sensor. Standard liveness detection cannot see injection attacks, unlike presentation attacks that involve holding a fake image in front of a camera, because the data arrives through the same pathway as legitimate camera input.
Why does liveness detection fail against injection attacks?
Physical spoofing is what liveness detection (PAD) looks for as it analyzes biometric data from the camera sensor. The sensor is bypassed entirely by injection attacks, which feed synthetic data at the software layer. Valid-looking data through the expected channel reaches the PAD algorithm, so it cannot distinguish that data from genuine sensor capture — software-layer injection is not what it was designed to address.
How common are injection attacks on KYC systems?
Against one financial institution's KYC flow, Group-IB documented 8,065 injection attacks between January and August 2025 — over 38 attacks per day. Seventeen face-swapping tools and 8 injection tools commercially available, most capable of bypassing standard biometric onboarding, were found by the WEF's January 2026 Cybercrime Atlas.
What does injection-resistant verification require?
Multiple layers make an effective defense: device attestation (cryptographically binding biometric data to real hardware), behavioral signal analysis (detecting session-level anomalies from automated tooling), NFC-based cryptographic document verification, and continuous post-onboarding monitoring by AI agents. No single layer is sufficient on its own.
Is ISO 30107-3 PAD certification protection against injection attacks?
No. Presentation attacks — physical spoofing in front of a camera — are what ISO 30107-3 certifies protection against. Injection attack resistance is not addressed. Injection testing results, device attestation capabilities, and behavioral analysis are what buyers should specifically ask vendors about — not PAD certification alone.
What regulatory requirements cover injection attacks?
Injection attacks becoming a primary threat largely postdates current regulatory frameworks — including MiCA's KYC requirements and the draft AMLR RTS. "Reliable" identity verification is required without specifying the technical architecture needed to counter injection attacks. Injection-resistant architecture should be implemented by organizations proactively rather than waiting for regulatory guidance to catch up with the threat.
Related Articles
Account Takeover Fraud Up 250%: Why Static KYC Fails
Account takeover fraud spiked 250% and cost $16B in 2024. Discover why one-time KYC verification is structurally powerless against post-onboarding attacks.
Face Alone Is No Longer Proof: Multimodal Liveness in KYC
Deepfake losses hit $3.7B in 2026. Here is why single-signal biometric liveness checks are failing — and what multimodal KYC verification requires.
One in 100: How Deepfakes Are Breaking ID Checks at Scale
LexisNexis: 1 in 100 failed identity checks involves a deepfake. At 100 billion annual checks, the math makes this a systemic infrastructure crisis.